Computer & Control Systems Department student with a strong passion for Cybersecurity, specializing in Reverse Engineering, Digital Forensics, and Malware Analysis. Enthusiastic about reversing complex systems, uncovering how they work, and analyzing malicious software to understand and mitigate security threats. I enjoy exploring real-world security cases and applying advanced problem-solving techniques to practical challenges. Beyond cybersecurity, I have broad interests in technology, including hardware, robotics, and innovation. I actively participate in Capture the Flag (CTF) competitions to sharpen my technical expertise, stay updated with the latest security trends, and continuously develop my skills in this dynamic field.
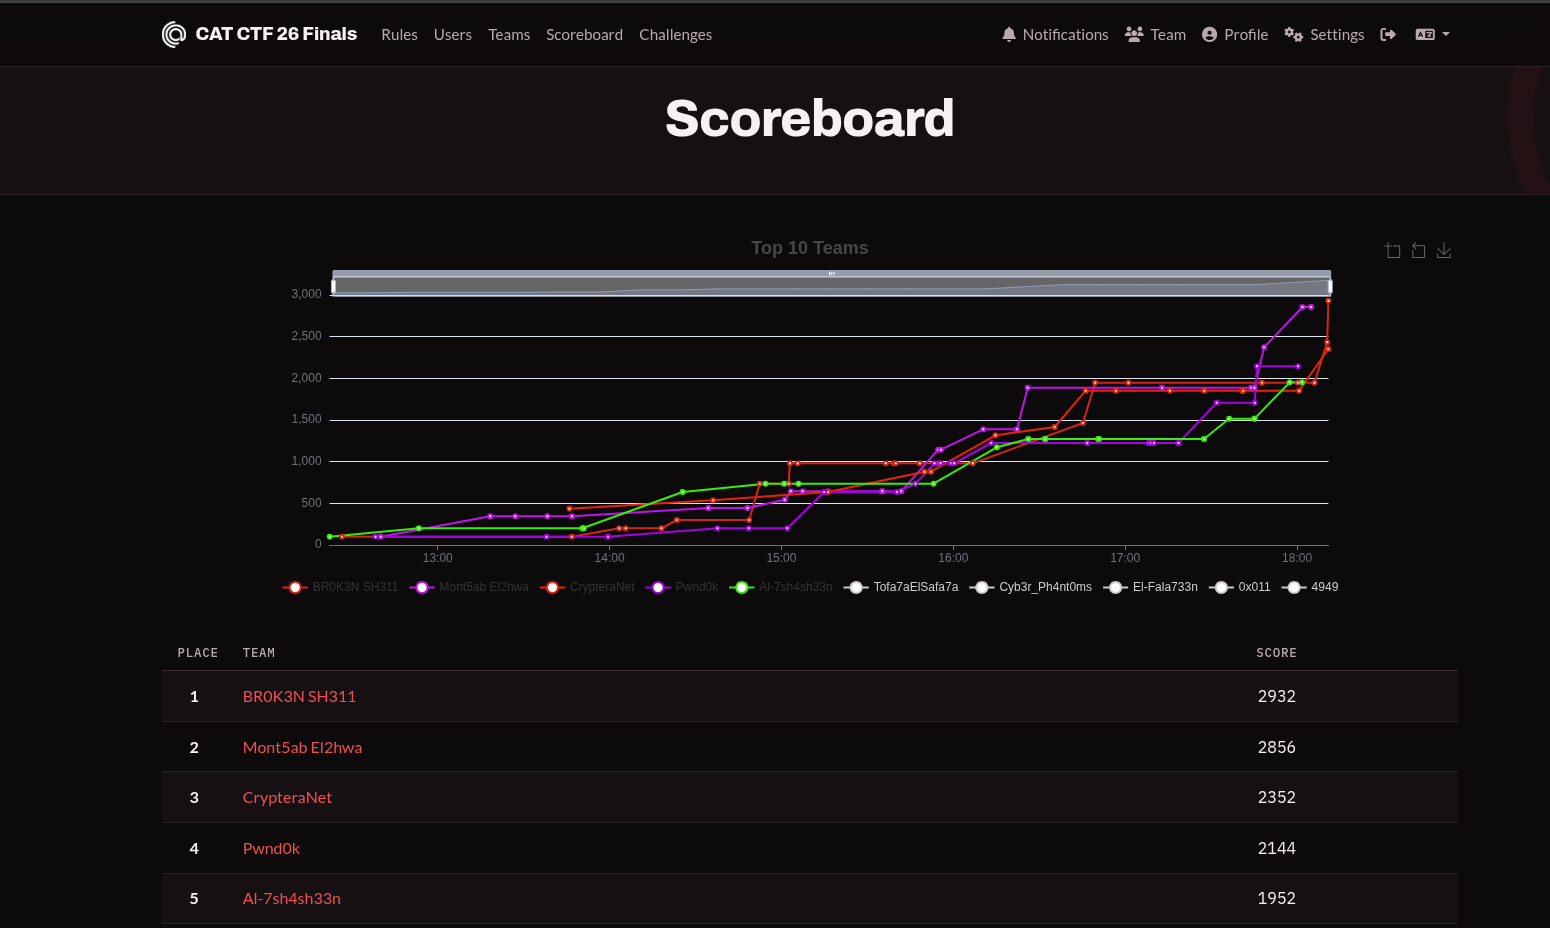
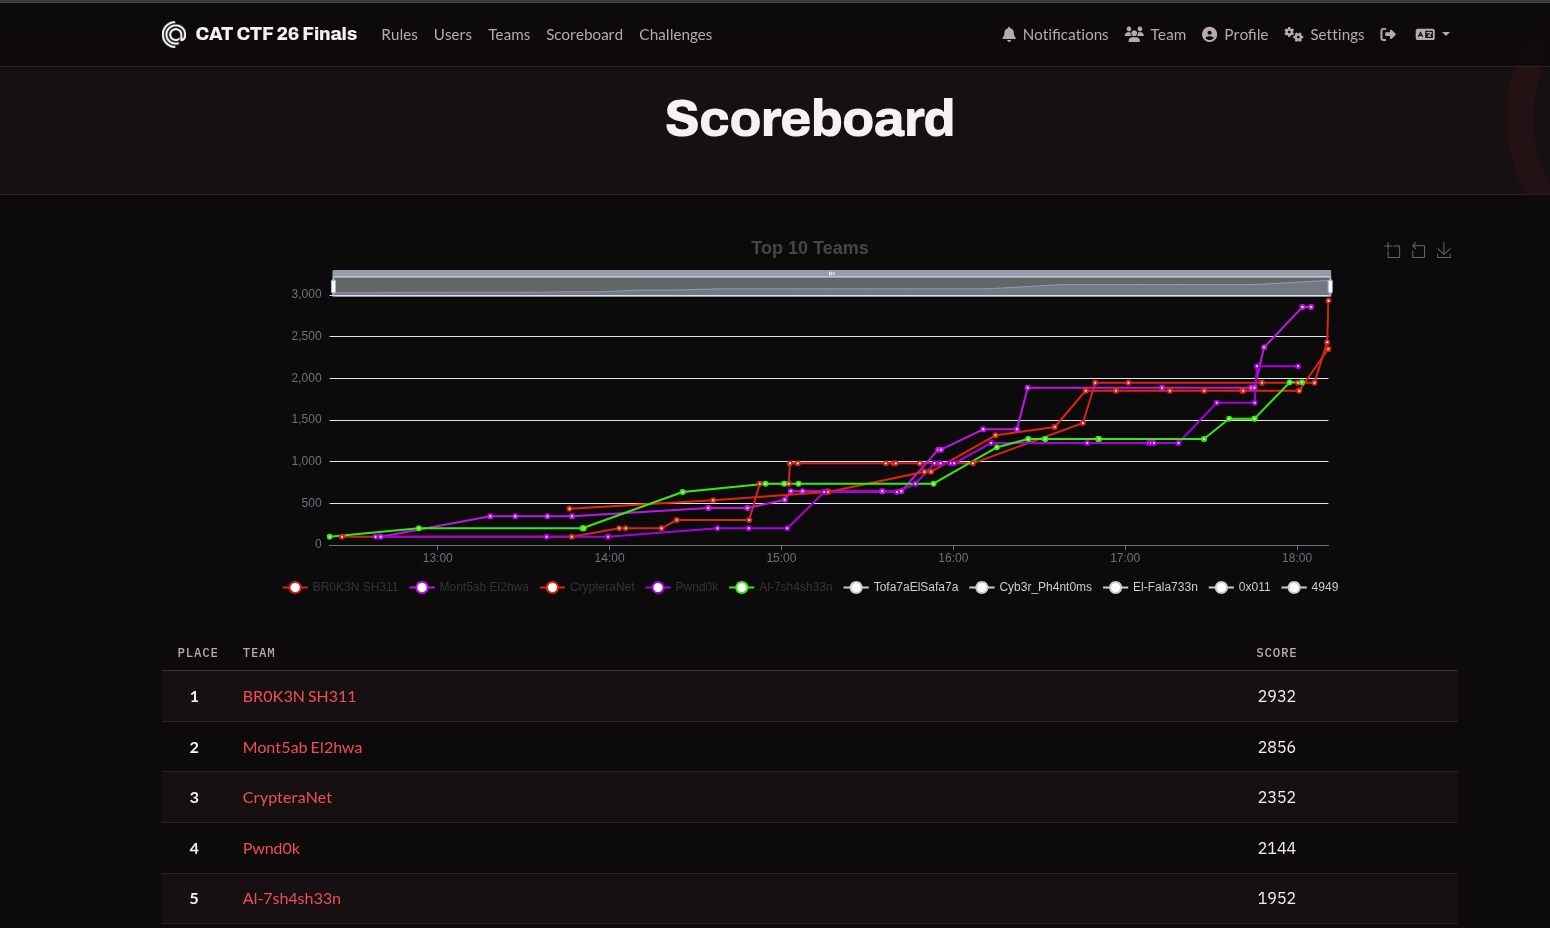
Walkthrough of the Devs beginning DFIR challenge at CAT CTF 26 Finals, analyzing FTK evidence, PowerShell history, and recovering DPAPI keys to access a...
Walkthrough of the 67 iq Sudoku reverse engineering challenge at CAT CTF 26 Finals, bypassing verification checks via IDA/GDB remote debugging to decrypt and...
Walkthrough of the CrackMe reverse engineering challenge at CAT CTF 26 Finals, analyzing the PE serial verification routine, bruteforcing encrypted blobs, and...
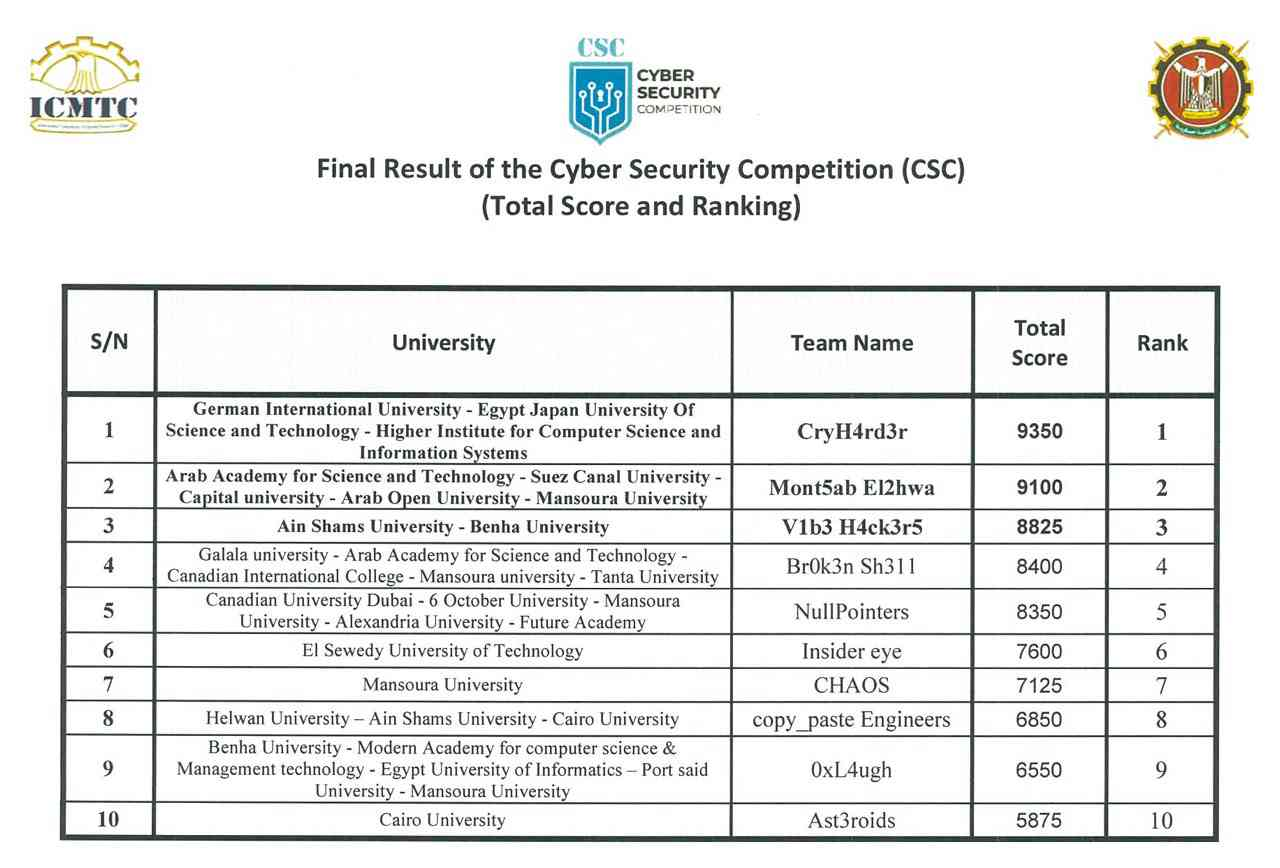
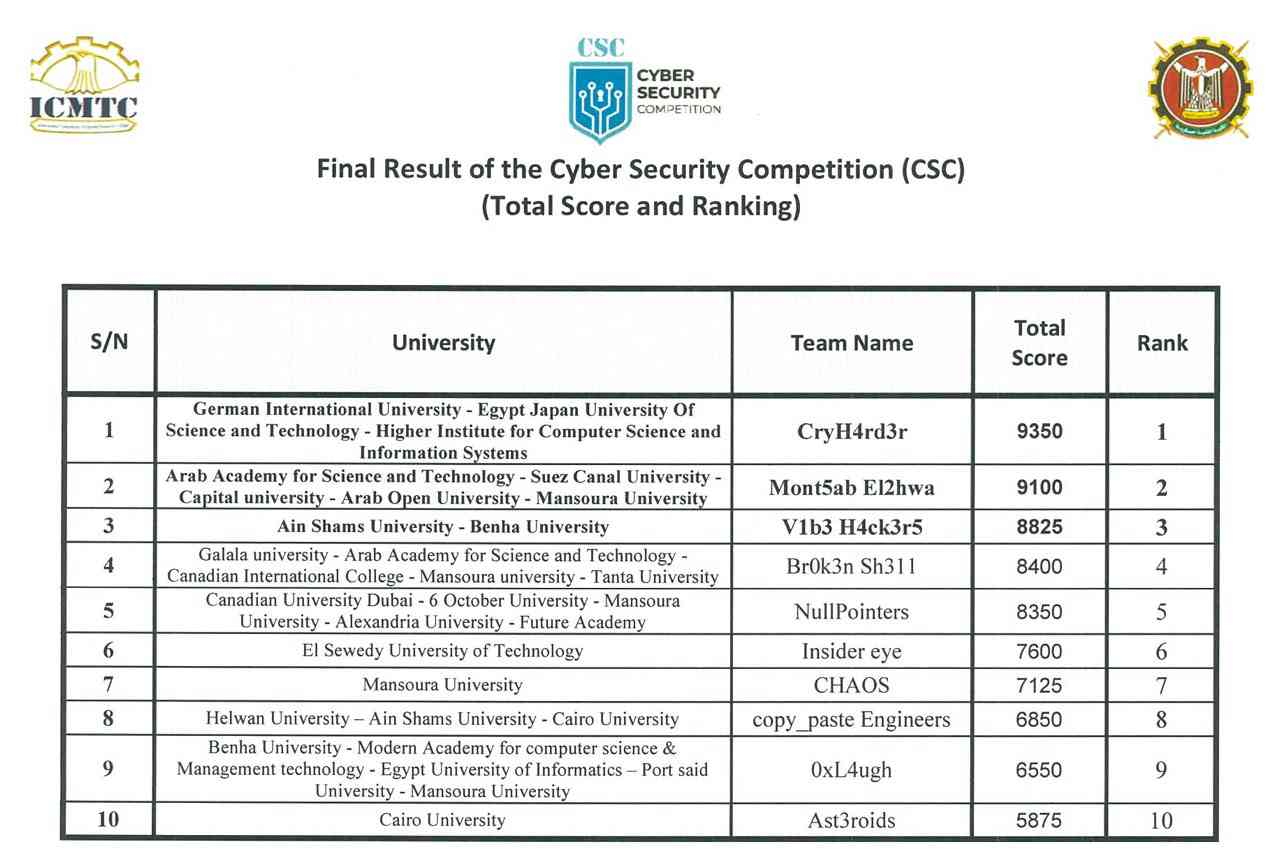
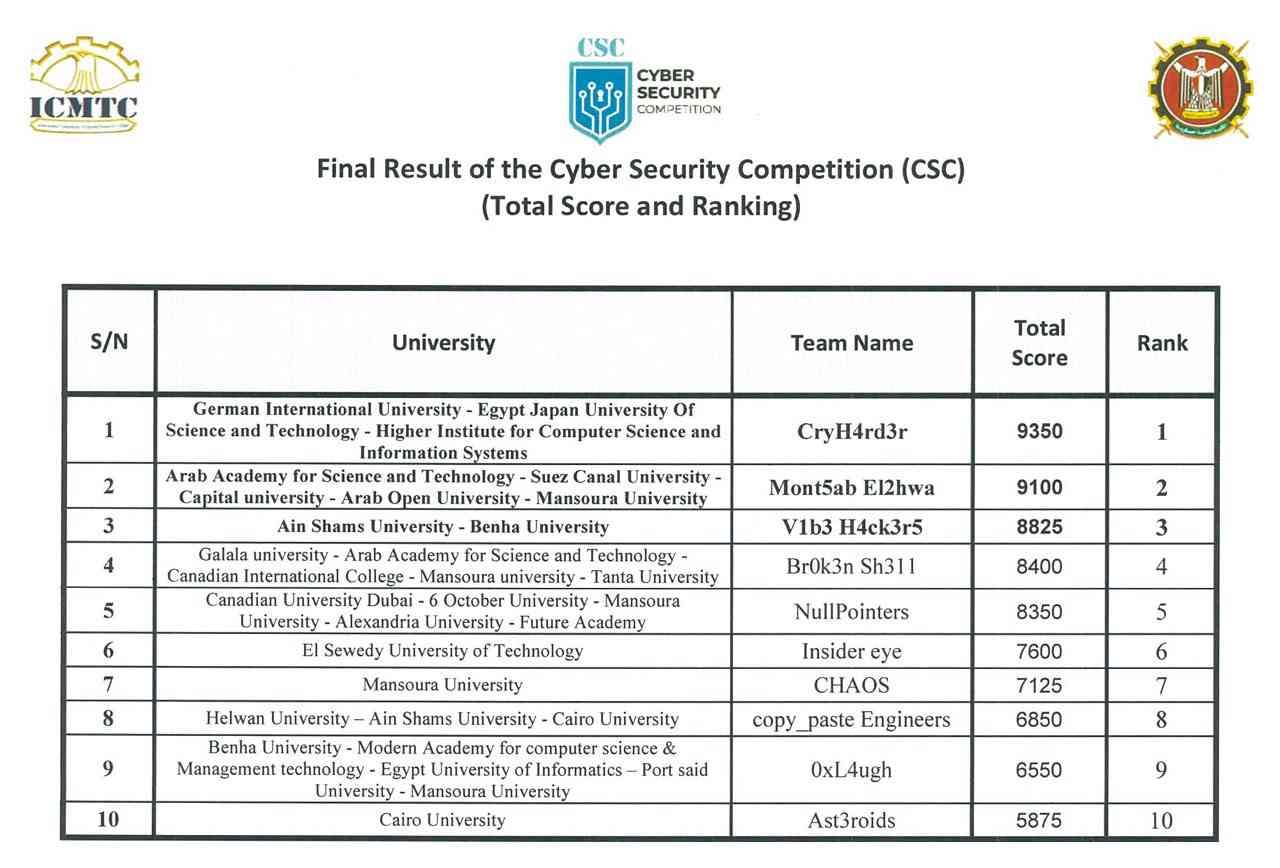
Walkthrough of the Infected ransomware memory forensics challenge at ICMTC Finals 2026, using Volatility 3 to extract malware artifacts, reversing Atac4D.dll,...
Walkthrough of The Empire is at risk challenge at ICMTC Finals 2026, analyzing network traffic and memory dumps to unpack PowerShell Empire C2 staging, decrypt...
Walkthrough of the idman reverse engineering challenge at ICMTC Finals 2026, analyzing a trojanized IDM installer, identifying the backdoored idmvs.dll, and...
category: Forensics / Reverse Engineering Ragab Ganber was finally caught. After his arrest, investigators seized two laptops: a personal Windows laptop and a...
Digital ForensicsDisk ForensicsMalware AnalysisReverse EngineeringCross-PlatformEYCC CTF 2026beginner-friendly